GRAPHENE sees the network
A passive, agentless intrusion-detection system for industrial control networks.
GRAPHENE is an advanced intrusion-detection system (IDS) for SCADA networks that works passively and non-intrusively. It is installed on every VLAN of the control network and monitors the traffic between all the assets, HMI servers, PLCs, RTUs and VFDs, without disturbing the industrial process.

The learning phase
After installation, a learning phase maps the network's assets, protocols, the kind and direction of each conversation and its bandwidth, and defines normal network behaviour as the baseline for spotting deviations.

Main capabilities
- Behavioural monitoring and detection of deviations from the normal operating curve
- Asset and protocol discovery and mapping
- Detection of firmware and logic changes, port scans, DDoS and malware
- Whitelisting of HMI operations and network access control (NAC)
- Continuous vulnerability assessment and protection of external devices
- Compatible with the leading SIEM platforms


Standards and sectors
Compatible with NIST SP 800-82 and 800-53, NERC CIP and ISA-99. Sector modules for energy and power stations, gas and oil refining, desalination, smart buildings, chemicals and pharma, and transport.
In the field
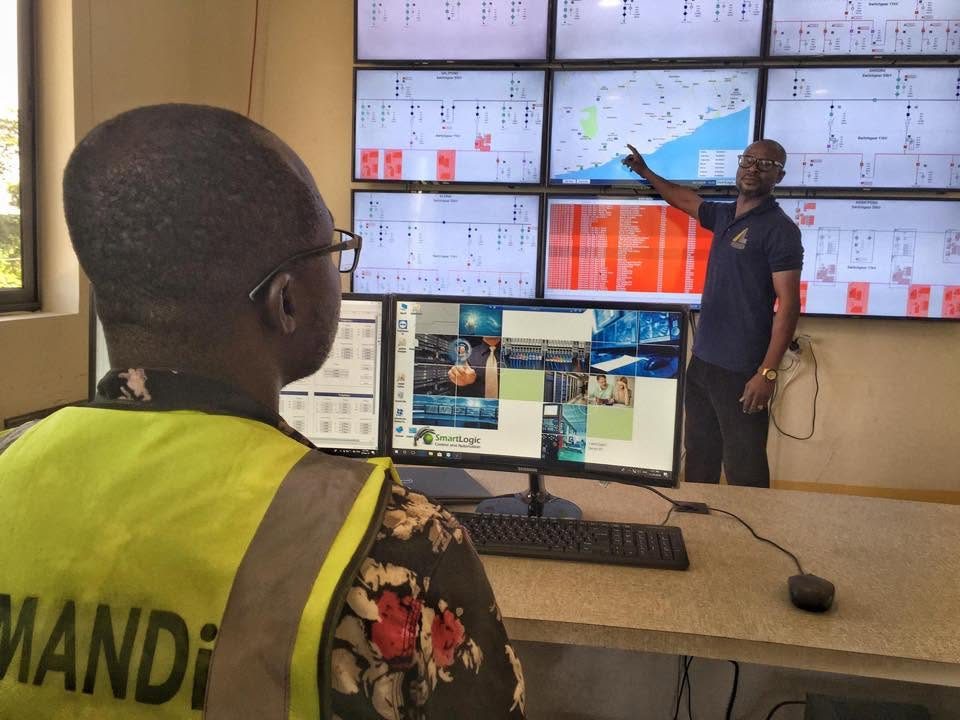
GRAPHENE runs in nine electricity substations in Ghana, monitoring the control networks, detecting intrusions and analysing the industrial protocols (Israel Defense, 2018).
Together with SPARTA
GRAPHENE hardware can be combined with the SPARTA module for combined protection: IDS at the network level, IPS and IDS on the HMI.